
 From strategy to launch, we design and build the products our clients grow on.See Case StudiesSee Case Studies
 Explore
- ServicesOur ServicesWhat We BuildMarketing sites & platformsCustom internal toolsAI features & automationDesign systems & rebrandsCampaign & content programsNot sure which team you need?Book a 30-minute discovery call with our product and engineering leads.


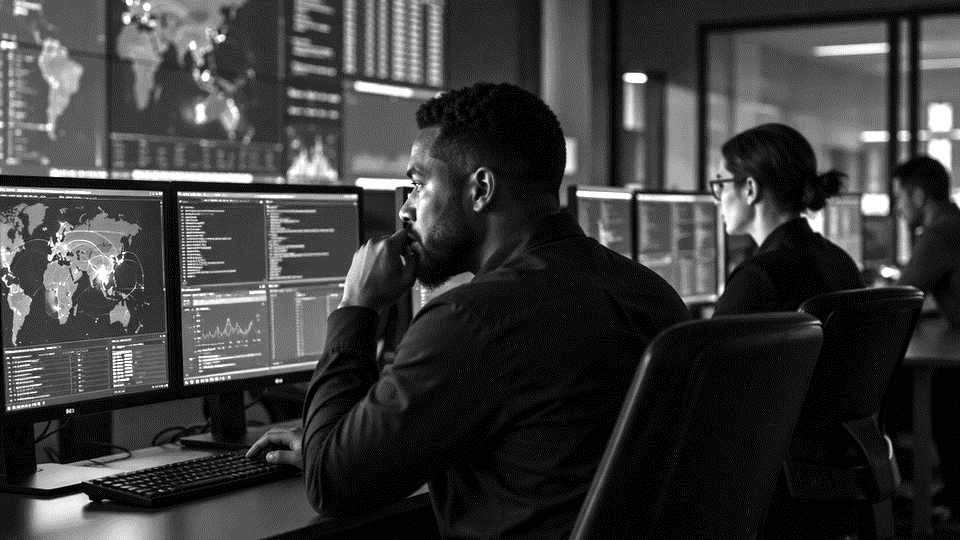
What Security Platforms teams need most
WHAT WE BUILD
Product & platform engineering

Role-Based Access
Roles defined by job, with the permissions each one actually needs.
Audit Trail & Evidence
Every sensitive action recorded with actor, time and target.
SSO & Directory Sync
Login through the customer's identity provider, with groups mapped.
Alert & Triage Workflows
Alerts with severity, an owner and a resolution record.
Data Retention Controls
Retention periods per data type, enforced and documented.
Customer Security Portal
Controls, evidence and subprocessor details published with dates.
Where Security Platforms teams lose time
A security product is sold to a buyer who assumes it will fail. Their team sends a questionnaire, asks for a pen test summary and wants to know who can see their data. The answers sit across a wiki, an old spreadsheet and one engineer's memory.
The system we build makes those answers easy to produce. Roles and permissions are explicit, every sensitive action writes an audit record, and a customer portal publishes the evidence behind each control with a date, an owner and a scope.
01
Questionnaires rebuilt each time
Every prospect sends a different security questionnaire and an engineer answers it from scratch, which slows deals and produces inconsistent claims.
02
Permissions nobody can explain
Access accumulates over time, and no one can say why a contractor account still holds admin rights on a production system.
03
Alert queues ignored
Security alerts land in a shared inbox with no owner or severity, and the team triages them when someone has time.
HOW THE BUILD RUNS
OUR PROCESS
Step 01
Walk the workflow
We sit with the people who do the work and follow one job from first contact to final invoice. The gaps show up quickly once nobody is describing them from memory.
Step 02
Model the data
Bookings, orders, patients or jobs become one set of records with clear owners. We agree on the fields before any screen gets built.
Step 03
Build in stages
The costliest step ships first, usually the one where revenue or time leaks. Each stage goes live while the next one is being built.
Step 04
Hand over and support
Your team gets training, written runbooks and a support window. We stay close through the first month of real use, then step back.
SYSTEMS WE CONNECT TO
INTEGRATIONS
We build around what you already run. These are the systems we most often read from, write to, or replace one part of, without asking your team to start over.
Identity providers
Billing and subscription systems
Data warehouses
Support and CRM tools
Observability and alerting
THE TARGET
2 wk
Sprint Cadence
Shippable increments on a predictable rhythm.
THE EXPERIENCE
99.9%
Uptime Target
Reliability engineered into every release.
THE COVER
90+
Lighthouse Score
Performance budget applied to customer-facing surfaces.
THE HANDOVER
24/7
Monitoring
Errors and regressions surfaced before customers report them.
OTHER SPECIALTIES
SaaS & Technology


QUESTIONS & ANSWERS
Questions about Security Platforms
The questions that come up before a saas & technology engagement starts.
How do you support security reviews?
We help assemble the evidence behind each control and put it in a customer-facing portal, so questionnaires start from documentation instead of a scramble.
Can role changes be audited?
Every permission change records who made it, when and against what. Access reviews become an export rather than an investigation.
Do you claim certifications for the product?
No. We build toward the standard your customers ask for and keep the evidence. Certification is your auditor's call, not ours.
Can we support customer-managed keys?
Where your cloud provider supports it, yes. Keys stay in the customer's account and access is logged, which answers a common requirement for buyers in regulated sectors without changing how the app encrypts data.
How do access reviews work?
Each role owner reviews their members on a schedule, and the decision is recorded. The review becomes an export with dates, which is what an auditor asks for rather than a screenshot.
Do you help with incident response planning?
We document the runbook, the notification path and the evidence to collect, then test it once before handover. Your team runs the process; we make sure the steps and contacts exist.
HOW WE HELP
The wider team behind this work
Most specialty builds draw on more than one service line. One team, one scope, no handoffs between vendors.


Talk to us about security platforms.
Tell us what your team runs today and where it breaks. A real person replies, usually the same day.
Start a conversation
Start a conversation
contact us
Let's Talk About Your Project
Scope the problem and its constraints
Review your current product and stack
Agree on timeline, team, and budget
Cover security and compliance needs
Plan integrations with your tools
Leave with a clear first milestone
edgeless solutions

edgeless solutions
edgeless solutions
edgeless solutions
edgeless solutions


